
jeffersongoncalves / laravel-gdpr-consent

GDPR consent ledger for Laravel: append-only proof of consent per purpose and version (Art. 7), withdrawal as easy as giving it, expiry, anonymous visitors claimed on login.
Package info
github.com/jeffersongoncalves/laravel-gdpr-consent
pkg:composer/jeffersongoncalves/laravel-gdpr-consent
Requires
- php: ^8.2
- illuminate/contracts: ^12.0|^13.0
- illuminate/database: ^12.0|^13.0
- illuminate/http: ^12.0|^13.0
- illuminate/routing: ^12.0|^13.0
- illuminate/support: ^12.0|^13.0
- illuminate/validation: ^12.0|^13.0
- jeffersongoncalves/laravel-gdpr: ^1.0
- spatie/laravel-package-tools: ^1.16
Requires (Dev)
- jeffersongoncalves/pest-plugin-database-migrations: ^1.0
- larastan/larastan: ^3.0
- laravel/pint: ^1.24
- orchestra/testbench: ^10.0|^11.0
- pestphp/pest: ^3.0|^4.0
- pestphp/pest-plugin-laravel: ^3.0|^4.0
Suggests
None
Provides
None
Conflicts
None
Replaces
None
README
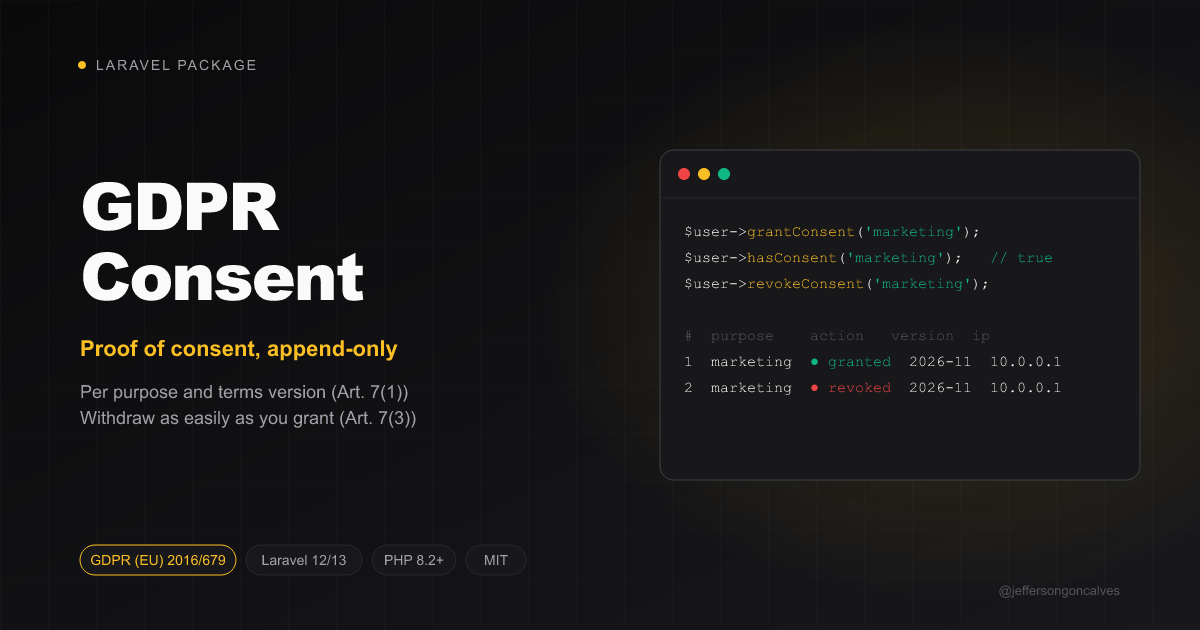
Consent ledger for the EU General Data Protection Regulation (GDPR, Regulation (EU) 2016/679). It is part of the laravel-gdpr suite.
Under the GDPR the controller must be able to demonstrate that consent was given (Art. 7(1)), and withdrawing consent must be as easy as giving it (Art. 7(3)). This package records every decision as a new row, and never updates or deletes a row:
- grants and revocations per purpose, with the terms version in force at the time;
- proof of consent: IP address, user agent, source, and custom metadata;
- when you bump a purpose's terms version, consents given under the old version stop counting;
- consents can expire after a period you configure;
- works for users (any Eloquent model) and for anonymous visitors (a random id stored in a cookie);
- an optional endpoint where your cookie banner can record each choice.
This package gives you tooling. It does not make you compliant on its own. You still need legal review for your purposes and terms.
Installation
composer require jeffersongoncalves/laravel-gdpr-consent
php artisan vendor:publish --tag="gdpr-consent-migrations"
php artisan migrate
php artisan vendor:publish --tag="gdpr-consent-config"
Configuration
// config/gdpr-consent.php
'purposes' => [
    'marketing' => ['version' => '2026-11', 'expires_after' => '1 year'],
    'analytics' => ['version' => '1'],
],
When purposes is set, unknown purposes are rejected. When it is empty, any purpose is accepted and no version is enforced.
Usage
use JeffersonGoncalves\GdprConsent\Concerns\HasConsents;

class User extends Authenticatable
{
    use HasConsents;
}

$user->grantConsent('marketing', source: 'signup-form', metadata: ['checkbox' => 'newsletter']);
$user->hasConsent('marketing');   // true
$user->revokeConsent('marketing');
$user->consents;                  // full history
For visitors who have no account, or from anywhere else:
use JeffersonGoncalves\GdprConsent\Facades\GdprConsent;

GdprConsent::grant($anonymousId, 'analytics');
GdprConsent::has($anonymousId, 'analytics');
GdprConsent::history($user, 'marketing');
Every decision dispatches JeffersonGoncalves\GdprConsent\Events\ConsentRecorded.
Endpoint for banners
Enable it with route.enabled => true, then send:
fetch('/gdpr/consent', {
    method: 'POST',
    headers: { 'Content-Type': 'application/json', 'X-CSRF-TOKEN': token },
    body: JSON.stringify({ purpose: 'analytics', granted: true }),
});
A logged-in user's choice is recorded on the user. A guest's choice is recorded under a random id, which is kept in an encrypted cookie (gdpr_consent_id).
When a guest logs in, their decisions move to the account. For each purpose, the guest's latest decision is copied onto the user as a new record, with source claimed and the guest id plus the original record id in its metadata. The original IP address, user agent and expiry are kept as the proof. A decision the user made after the guest's one wins. The guest rows stay untouched, because the ledger is append-only. This runs on Laravel's Login event when the endpoint is enabled. Turn it off with route.claim_on_login => false, or call it yourself:
GdprConsent::claim($anonymousId, $user); // returns the records it created
Append-only
Calling update() or delete() on a ConsentRecord throws an exception. The one exception is the personal data columns (ip_address, user_agent): the records are declared with laravel-gdpr's #[PersonalData], so you can still clear those columns with $record->anonymizePersonalData().
Testing
composer test
Changelog
See CHANGELOG.
License
The MIT License (MIT). See License File.