
jeffersongoncalves / filament-security-headers

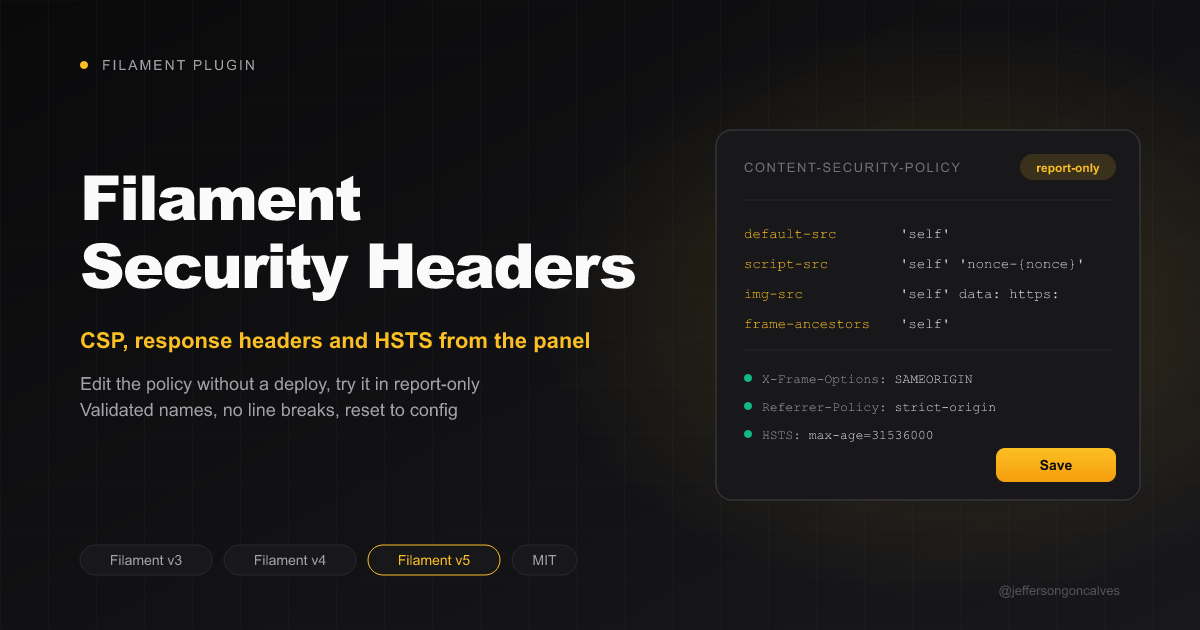
Filament settings page for laravel-security-headers: edit the Content Security Policy, response headers and HSTS from the panel, with a report-only mode to try a policy before enforcing it.
Package info
github.com/jeffersongoncalves/filament-security-headers
pkg:composer/jeffersongoncalves/filament-security-headers
Requires
- php: ^8.2
- filament/filament: ^5.3
- filament/spatie-laravel-settings-plugin: ^5.3
- jeffersongoncalves/laravel-security-headers: ^2.0
- spatie/laravel-package-tools: ^1.16
- spatie/laravel-settings: ^3.0
Requires (Dev)
- larastan/larastan: ^3.0
- laravel/pint: ^1.0
- orchestra/testbench: ^10.0|^11.0
- pestphp/pest: ^3.0|^4.0
- pestphp/pest-plugin-laravel: ^3.0|^4.0
Suggests
None
Provides
None
Conflicts
None
Replaces
None
This package is auto-updated.
Last update: 2026-10-10 19:44:32 UTC
README
Filament Security Headers
A Filament settings page for jeffersongoncalves/laravel-security-headers: edit the Content Security Policy, the response headers and HSTS from the panel instead of a config change and a deploy.
- CSP directives as key/value pairs, the
{nonce}placeholder included, plus the report URI - Report-only mode to try a new policy (
Content-Security-Policy-Report-Only) before enforcing it - Response headers (
X-Frame-Options,Referrer-Policy,Permissions-Policy...): edit, add, or leave a value empty to drop one - HSTS: on/off, max-age, subdomains, preload
- Reset to config at any time
Until the page is saved, nothing changes: the middleware keeps using config/security-headers.php, and the page opens with those values. Header and directive names are validated and line breaks are rejected (no response splitting).
Compatibility
| Branch | Filament | Package version |
|---|---|---|
| 1.x | 3.x | ^1.0 |
| 2.x | 4.x | ^2.0 |
| 3.x | 5.x | ^3.0 |
Installation
composer require jeffersongoncalves/filament-security-headers:"^3.0"
php artisan vendor:publish --tag=filament-security-headers-settings-migrations
php artisan migrate
Set up laravel-security-headers first (the SecurityHeaders middleware on your routes).
Usage
use JeffersonGoncalves\Filament\SecurityHeaders\SecurityHeadersPlugin;

public function panel(Panel $panel): Panel
{
    return $panel
        ->plugins([
            SecurityHeadersPlugin::make()
                // optional: one of your panel's own groups (string or closure)
                ->navigationGroup(fn (): string => __('admin.navigation.settings')),
        ]);
}
The saved values are read once per request (one settings query; enable the spatie/laravel-settings cache to skip it). The header is built on every request — including pages served by a full-page cache such as laravel-page-cache — so a saved change applies right away; flushing the page cache does not change it.
Tightening the policy safely
- Turn on report-only, change the directive (e.g. swap
'unsafe-inline'for'nonce-{nonce}'inscript-src) and save. - Browse the site and watch the browser console: report-only logs every violation without blocking anything.
- Fix what violates (inline scripts without the nonce, Alpine expressions that need
'unsafe-eval'— see Nonces and Alpine.js / Livewire without 'unsafe-eval'), then turn report-only off.
If something breaks after enforcing, put the old value back (or Reset to config) — no deploy needed. Proxies may also add scripts of their own (e.g. Cloudflare's Google tag gateway injects inline GTM without the nonce); check the page as a real browser receives it.
Requirements
- PHP 8.2 or higher
- Filament 5.x
- jeffersongoncalves/laravel-security-headers 2.x
Changelog
Please see CHANGELOG for more information on what has changed recently.
Contributing
Please see CONTRIBUTING for details.
Security Vulnerabilities
Please review our security policy on how to report security vulnerabilities.
Credits
License
The MIT License (MIT). Please see License File for more information.