
jeffersongoncalves / filament-gdpr-audit-log

Filament plugin for laravel-gdpr-audit-log: the GDPR accountability log in your panel, read-only, with who viewed, changed, exported or erased personal data and a one-click hash chain check.
Package info
github.com/jeffersongoncalves/filament-gdpr-audit-log
pkg:composer/jeffersongoncalves/filament-gdpr-audit-log
Requires
- php: ^8.2
- filament/filament: ^5.3
- jeffersongoncalves/filament-plugin-core: ^3.0
- jeffersongoncalves/laravel-gdpr-audit-log: ^1.0
- spatie/laravel-package-tools: ^1.16
Requires (Dev)
- jeffersongoncalves/pest-plugin-database-migrations: ^1.0
- larastan/larastan: ^3.0
- laravel/pint: ^1.0
- orchestra/testbench: ^10.0|^11.0
- pestphp/pest: ^3.0|^4.0
- pestphp/pest-plugin-laravel: ^3.0|^4.0
Suggests
None
Provides
None
Conflicts
None
Replaces
None
README
Filament GDPR Audit Log
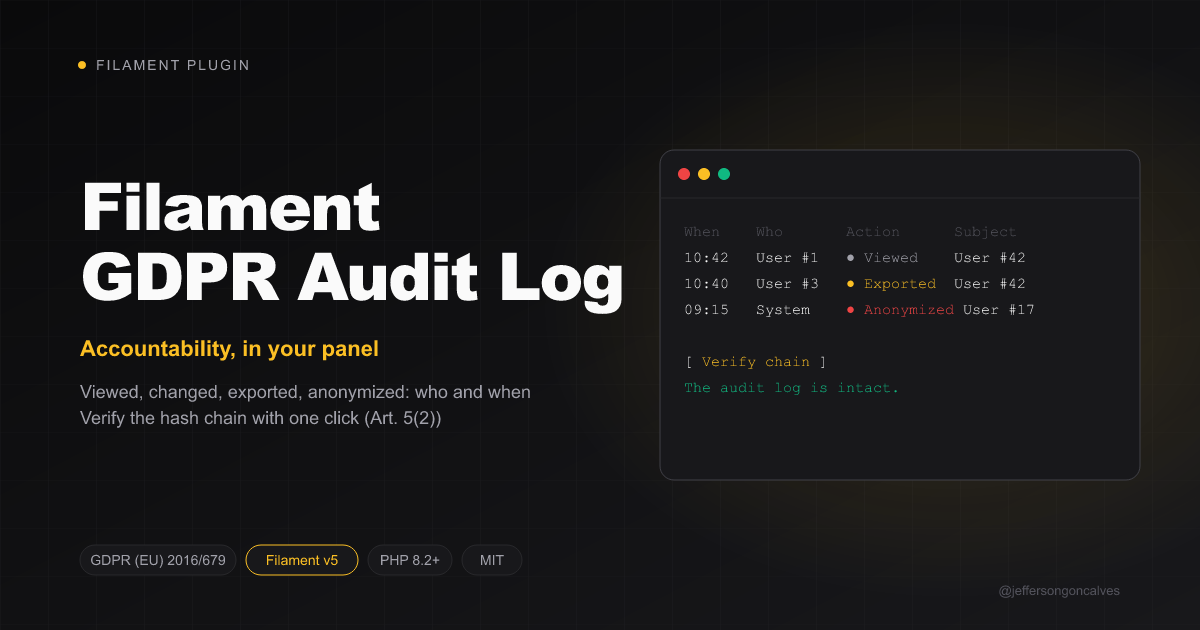
Browse the audit trail of laravel-gdpr-audit-log from your Filament panel: who viewed, changed, exported or anonymized whose personal data, when and why. You can also check that nobody tampered with it.
Features
- Every entry: when, who, action, data subject, columns (names only, never values) and purpose.
- Filters by action and by data subject model.
- View page with the IP address, user agent, metadata and the entry's hash.
- Who opens the list or an entry, and who verifies the chain, is logged too.
- Verify chain: checks the hash chain and tells you which entry was altered, removed or inserted.
- Read-only, like the log itself.
- 19 languages. Custom actions you record are shown as they are.
Compatibility
| Plugin Version | Filament |
|---|---|
| 1.x | 3.x |
| 2.x | 4.x |
| 3.x | 5.x |
Installation
You can install the package via composer:
composer require jeffersongoncalves/filament-gdpr-audit-log:"^3.0"
php artisan vendor:publish --tag="gdpr-audit-log-migrations"
php artisan migrate
Usage
use JeffersonGoncalves\Filament\GdprAuditLog\GdprAuditLogPlugin;

public function panel(Panel $panel): Panel
{
    return $panel
        ->plugins([
            GdprAuditLogPlugin::make()
                ->navigationGroup('GDPR')             // default: no group
                ->navigationSort(50)
                ->navigationIcon('heroicon-o-document-magnifying-glass')
                ->slug('audit-log')
                ->logViews(),                         // log who reads the log (default: on)
        ]);
}
All fluent methods are optional. Reading the log is logged too, with the purpose Audit log review: opening the list or an entry adds a viewed entry (its subject is the entry opened), and checking the chain adds a verified entry with the result. Turn it off with ->logViews(false).
The resource has no authorization of its own: register it only on panels whose users may read the audit log, or add a policy for
JeffersonGoncalves\GdprAuditLog\Models\AuditLog.
Testing
composer test
Changelog
Please see CHANGELOG for more information on what has changed recently.
Contributing
Please see CONTRIBUTING for details.
Security Vulnerabilities
Please review our security policy on how to report security vulnerabilities.
Credits
License
The MIT License (MIT). Please see License File for more information.